This approach is key to safe communication protocols like HTTPS, guaranteeing that information remains reliable even in transit. The distribution of keys between two or more entities concerned within the communication. The course of may involve a Key Technology or Key Agreement, the place a model new key’s produced as a perform of the secret (key) information possessed by the person speaking parties. The article additionally extends these obligations to certificate management, requiring monetary entities to hold up an up-to-date register and guarantee certificates are renewed earlier than they expire.
Kpi Administration: A Complete Introduction
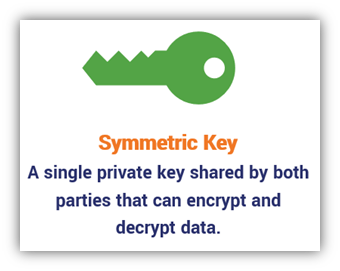
Be Part Of this webinar to explore sensible strategies for operating and governing AI brokers responsibly at scale, with skilled insights on observability, threat management and accountable AI operations. Key distribution is especially challenging for symmetric keys as a result of they must all the time remain secret. If DSA have to be used, select a minimum of 2048-bit keys with a 224-bit or 256-bit q, although 3072-bit keys are strongly most well-liked. For more particulars on key length recommendations for EdDSA or ECDSA, discuss with Cryptographic keylengths and Elliptic-Curve Cryptography. Monthly updates on CSA Chapters, together with native occasions, chapter activities, leadership highlights, and opportunities to connect along with your regional cloud security neighborhood.
What Is Vital Management?
It is a fundamental part in defending delicate data from unauthorized access and ensuring its integrity. When it comes to securing your confidential data, encryption is universally acknowledged as a requirement, however it’s not a silver bullet for security. Attackers are looking for these cryptographic keys as they enable access to the encrypted data.
Key Rotation And Lifecycle Management
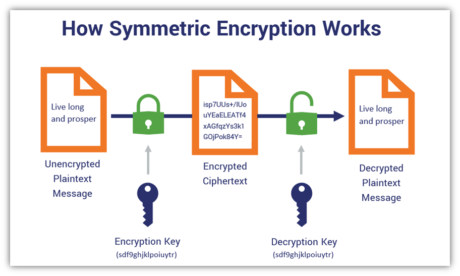
Encryption depends on complex algorithms, scrambling information so that it remains inaccessible to those that lack the personal keys required for decryption. Key generation involves utilizing a secure algorithm to create a cryptographic key, which is basically a string of random or pseudorandom bits or numbers. Making Certain that keys are random and unpredictable helps mitigate weaknesses that can compromise the complete encryption course of. 160-bit curves, such as secp160r1, have non-public keys of a hundred and sixty bits and public keys that range from 161 to 320 bits depending on encoding (compressed or uncompressed). Such small curves are not thought of safe, as they supply around eighty bits of security, falling beneath fashionable cryptographic requirements.
Deprecated Ecc Curves↑
- Centralized methods, usually called Key Administration Techniques KMS or Hardware Safety Modules HSM, automate these processes.
- If a PRNG lacks sufficient entropy or follows a deterministic pattern, attackers might predict or reconstruct personal keys, compromising the complete cryptographic system.
- This approach is fundamental to safe communication protocols like HTTPS, guaranteeing that information remains reliable even in transit.
- Organizations encrypt knowledge at relaxation and in transit to guard it from theft and to satisfy rules.
This complexity could make it difficult to guarantee that all keys are properly secured, tracked and maintained throughout their lifecycle. Diffie-Hellman key trade typically depends on predefined prime groups, similar to those from RFC 3526, to simplify implementation. Nonetheless, if widely used DH primes are reused throughout multiple methods, it may possibly compromise safety. The harvest now, decrypt later risk https://indiana-daily.com/leading-automated-cryptocurrency-trading-software-and-its-benefits.html makes this urgent for anyone handling information with long-term sensitivity.
